Deliverability and compliance
Email marketing compliance for venues
In the US, CAN-SPAM lets you email guests without asking first, as long as every message identifies you honestly and you honor opt-outs within 10 business days. Asking anyway builds the better list, and it protects your sending reputation too, because spam complaints are one of the signals mailbox providers act on.
What does US law require before you email guests?
Less than you might expect. CAN-SPAM, the federal law on commercial email enforced by the FTC (the Federal Trade Commission), is an opt-out law: you do not need a guest's permission before you send. What it regulates is the message itself, and what happens when someone says stop.
Every commercial email has to identify the sender honestly, avoid a misleading subject line, include a valid physical postal address and give the recipient a clear way to opt out. You then have to honor an opt-out within 10 business days, and you stay responsible for email others send on your behalf.
This guide explains the rules in general terms so you can ask the right questions. It is not legal advice, and state laws and the rules on texting add to it: your own attorney should confirm what applies to you.
If consent is not required, why ask for it?
Because the list you send to decides where your email lands. Mailbox providers watch how recipients react, and people who chose to hear from you open, click and stay subscribed, while people who never asked are more likely to ignore you or report you as spam.
Asking also gives you something to show. An opt-in checked by the guest at the login, timestamped and stored with the wording they saw, answers "I never signed up" with a record rather than an argument.
And if your group has venues in the UK, or markets to guests there, consent is the legal standard, so a list built on it works everywhere you operate.
Wording an opt-in at the login page: the WiFi email capture guide
What changes for guests in the UK?
There, the starting point is consent. PECR (the Privacy and Electronic Communications Regulations) generally requires a person's consent before you send them marketing by email or text, and UK GDPR governs how you collect, keep and erase their data. Consent has to be a clear, positive choice: a pre-checked box does not count, and nor does accepting the WiFi terms.
The UK's soft opt-in exception is narrow. It covers existing customers who bought something similar from you and were given a chance to refuse marketing; it does not cover prospects, bought lists or everyone who joined your WiFi, because a login is not a sale.
Why not buy or rent an email list?
Because nobody on it chose you. Whatever the law allows, the people on a bought list did not ask to hear from your venue, so they are likely to ignore you, unsubscribe or report you as spam. In the UK, consent is given to a named sender, so someone else's list rarely carries consent to hear from you at all.
The cost lands on your sending reputation. Old and mistyped addresses bounce, abandoned ones can be used as spam traps, and complaints count against you with mailbox providers. A small list of guests who asked to hear from you does more than a large one that did not.
- Nobody on a bought list asked to hear from your venue
- Old and mistyped addresses bounce, and bounces count against you
- Spam complaints from people who never chose you count against your domain
What decides whether your email reaches the inbox?
Three things: whether mailbox providers can confirm the email is really from you, whether the people you send to want it, and whether you keep your list clean. Authentication covers the first: SPF and DKIM show the email came from a server and a domain you control, and DMARC tells providers what to do with email that fails those checks.
The largest providers have made this a requirement rather than advice. Google's sender guidelines, in force since 2024, ask anyone sending more than 5,000 messages a day to Gmail accounts to authenticate with SPF, DKIM and DMARC, to offer one-click unsubscribe in marketing email and to keep spam complaints below 0.3%. Yahoo set similar requirements at the same time.
Then keep the list clean. Remove addresses that hard bounce, stop emailing anyone who complains, and stop sending to guests who have ignored you for a long time, because email that nobody opens tells providers it is not wanted.
- SPF: lists the servers allowed to send email for your domain
- DKIM: signs each email so providers can check it was not changed on the way
- DMARC: tells providers what to do with email that fails those checks
- One-click unsubscribe in every marketing email
How do you keep consent records you can prove?
Record five things for every opt-in: who agreed, when, to what wording, where (which venue, which form or login page) and for which channel. If a guest says "I never signed up", that record is your answer.
Withdrawal needs the same care. An unsubscribe has to take effect at once and stay in effect, which means it must survive the next import of an old spreadsheet. Keep a suppression list of everyone who has opted out, and check it before every send, not only when the campaign is approved.
Finally, do not keep data longer than you need it. Set a retention period for guests who stop engaging, write it down and apply it; for guests in the UK, UK GDPR requires you to. When a guest asks to be erased, erase them everywhere you hold their data, keeping only what you need to make sure they are not emailed again.
- Who: the guest's email address
- When: the date and time they agreed
- Wording: the exact text they saw, and its version
- Where: the venue, and the login page or form
- Channel: email, text or WhatsApp, each recorded separately
How Purple Engage does it
Compliance in Purple Engage
Purple Engage is the consent authority for your email, texts and WhatsApp: the one place every send checks. It supports your own legal advice rather than replacing it.
Consent per channel, with its source
One record per guest, channel, subscription group and purpose, so a yes to email is never read as a yes to texts or WhatsApp.Checked twice
Consent is checked when a campaign is approved and again just before each email goes, so a guest who unsubscribes in between is left out.Receipts and a proof pack
A receipt for every consent decision names the wording shown, the lawful basis, the source and the venue. A proof pack gathers the evidence for one campaign, one guest or a date range.Opt-outs that stay opted out
The suppression list survives re-import, a hard bounce suppresses the address, a spam complaint opts the guest out of every email group, and every marketing email has one-click unsubscribe.Your own authenticated domain
Email goes from your own sending domain, re-checked every 10 minutes, through SendGrid's EU region by default. Past its threshold, a reputation score pauses sending.Retention and erasure
Set a retention period in months, and any visit, click or form restarts the clock. Erasure runs through more than 30 registered routines, one for each place guest data is held.
Guides
Guides on email compliance
The first guides on email compliance are being written. Until they are published, these guides from the library cover related ground.
Related guides from the library
 Compliance
CAN-SPAM compliance for US restaurants and venues
 Compliance
Email deliverability basics for venue marketers
 Compliance
Managing consent and unsubscribes for venue email
Managing email consent correctly is the difference between a high-converting guest database and a GDPR liability.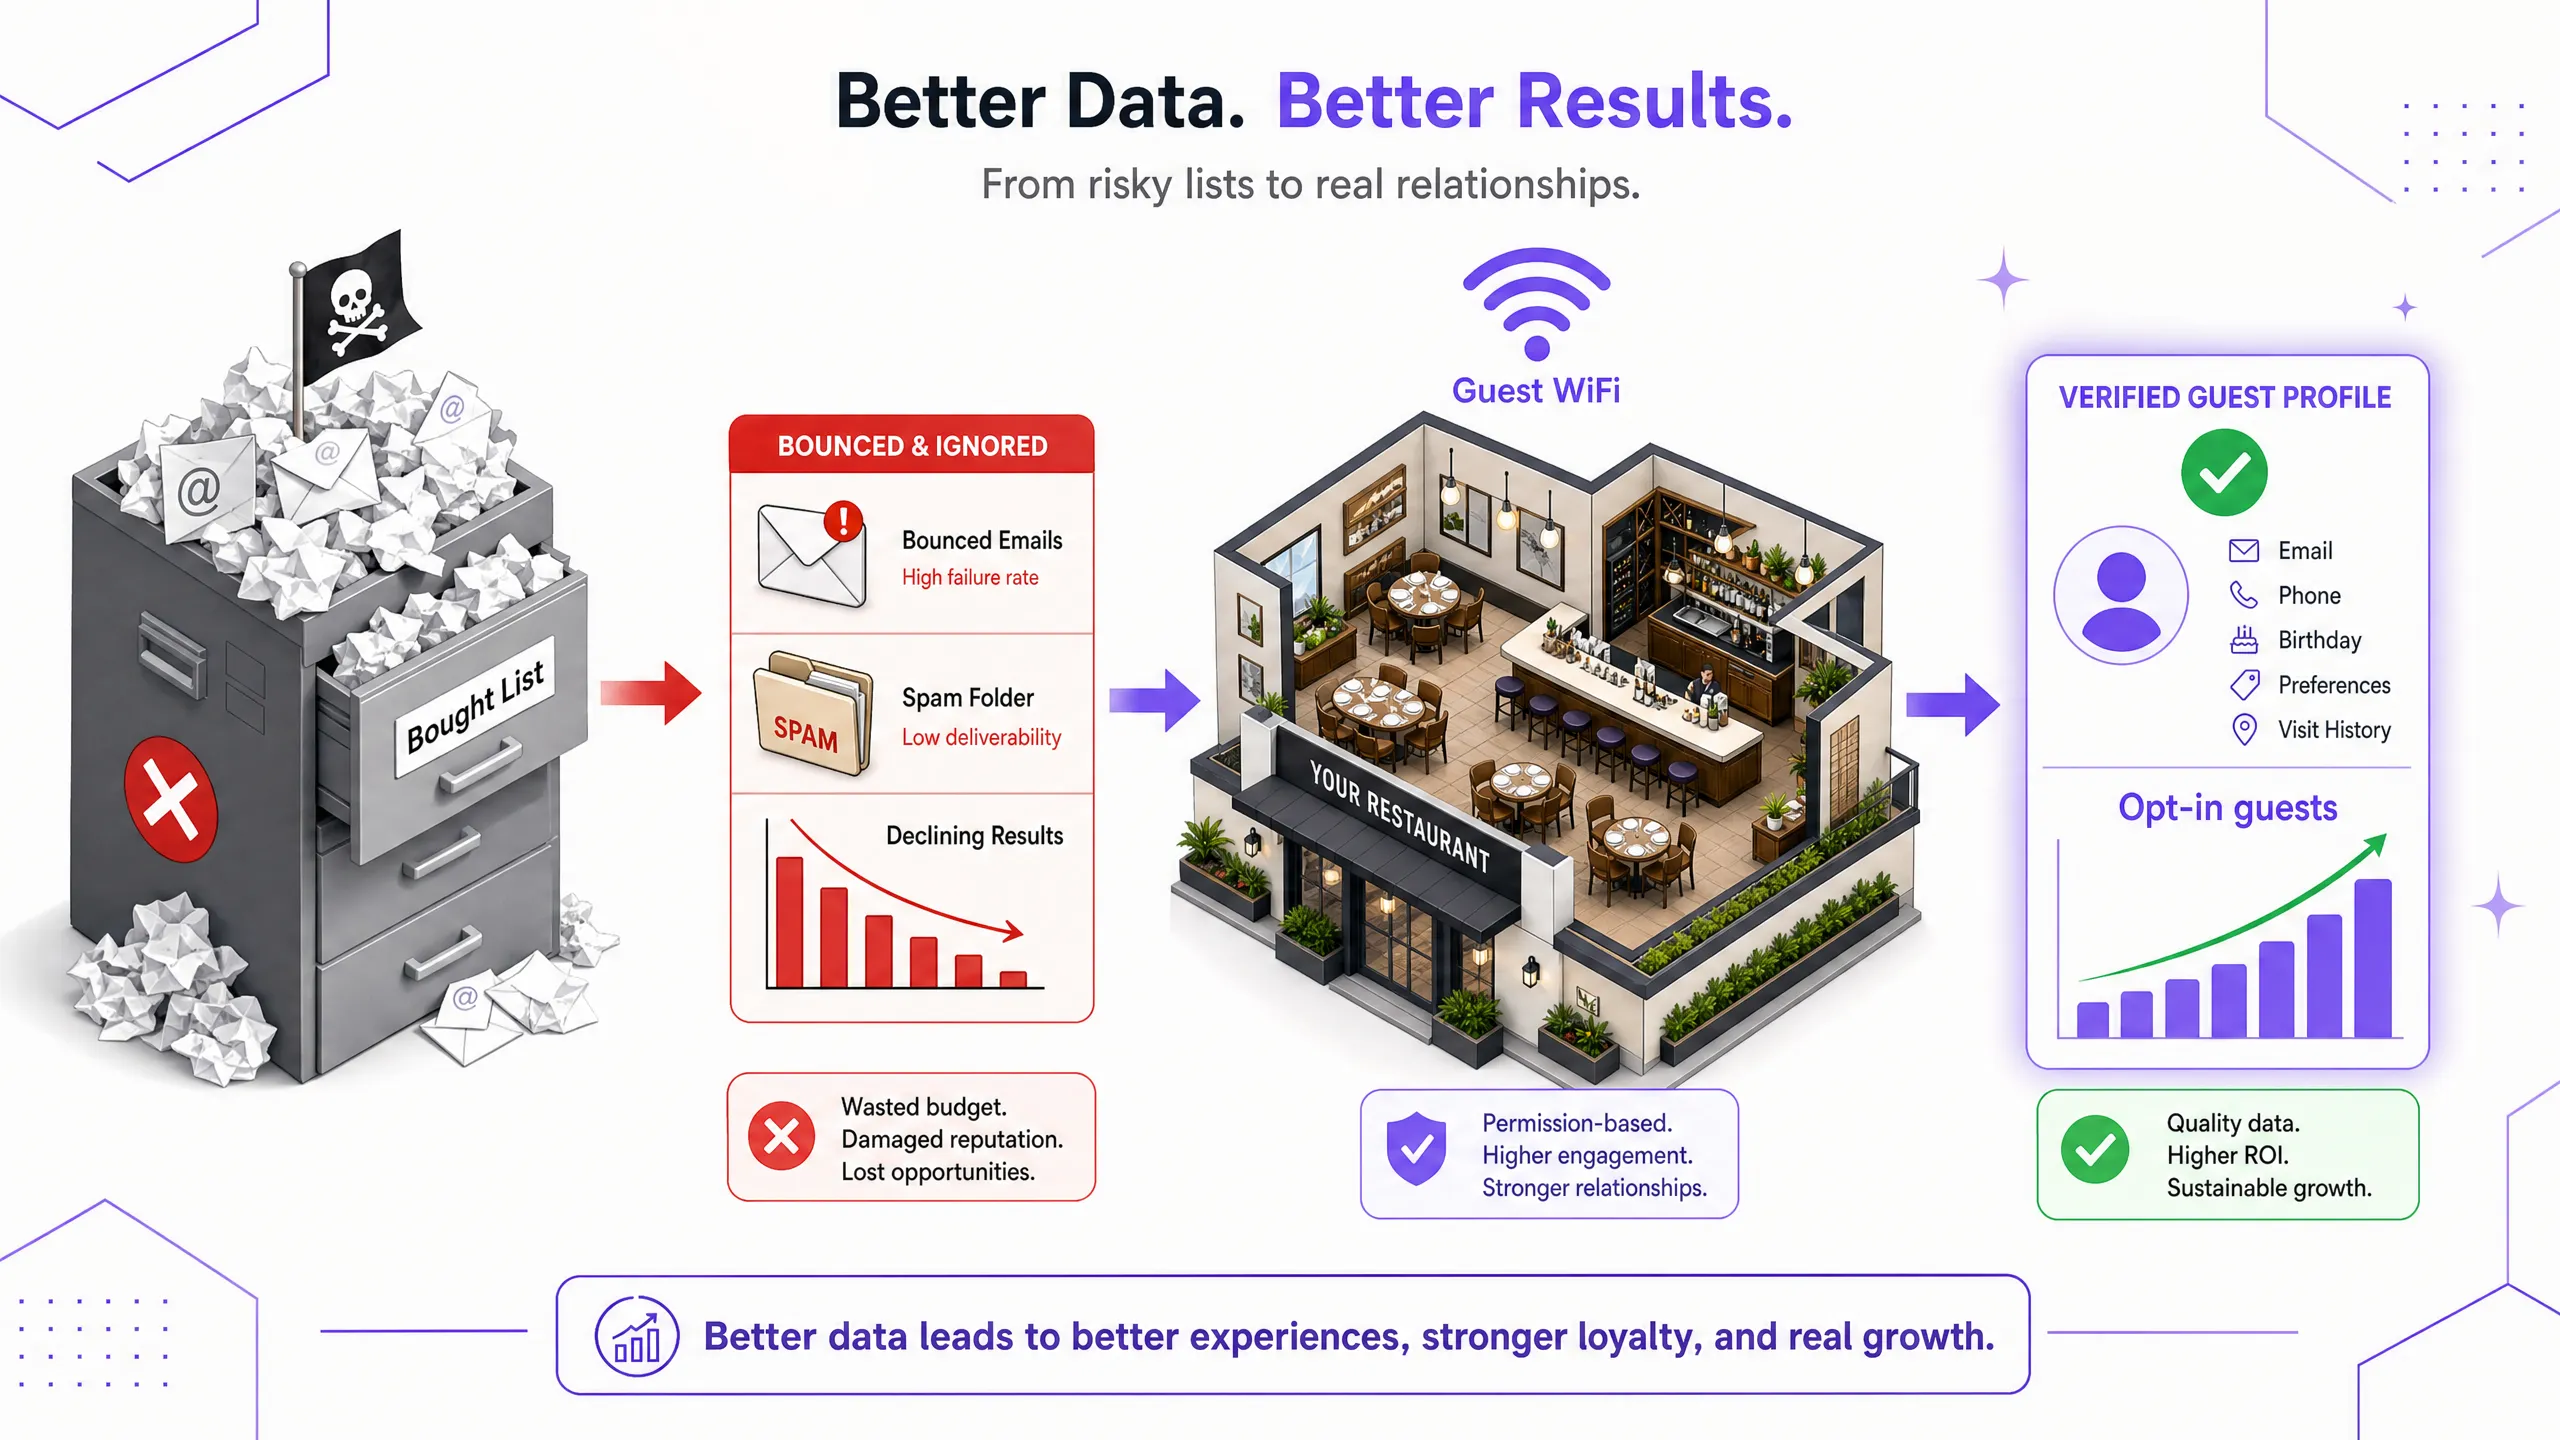 Compliance
Why purchased email lists fail venues
Buying email lists is one of the fastest ways to damage your sender reputation, violate GDPR, and waste marketing budgets. Compliance
The TCPA and CAN-SPAM and the soft opt-in: email marketing rules for venues
This guide explains what the TCPA and CAN-SPAM require for venue email marketing and why the soft opt-in exception is structurally insufficient for physical venues.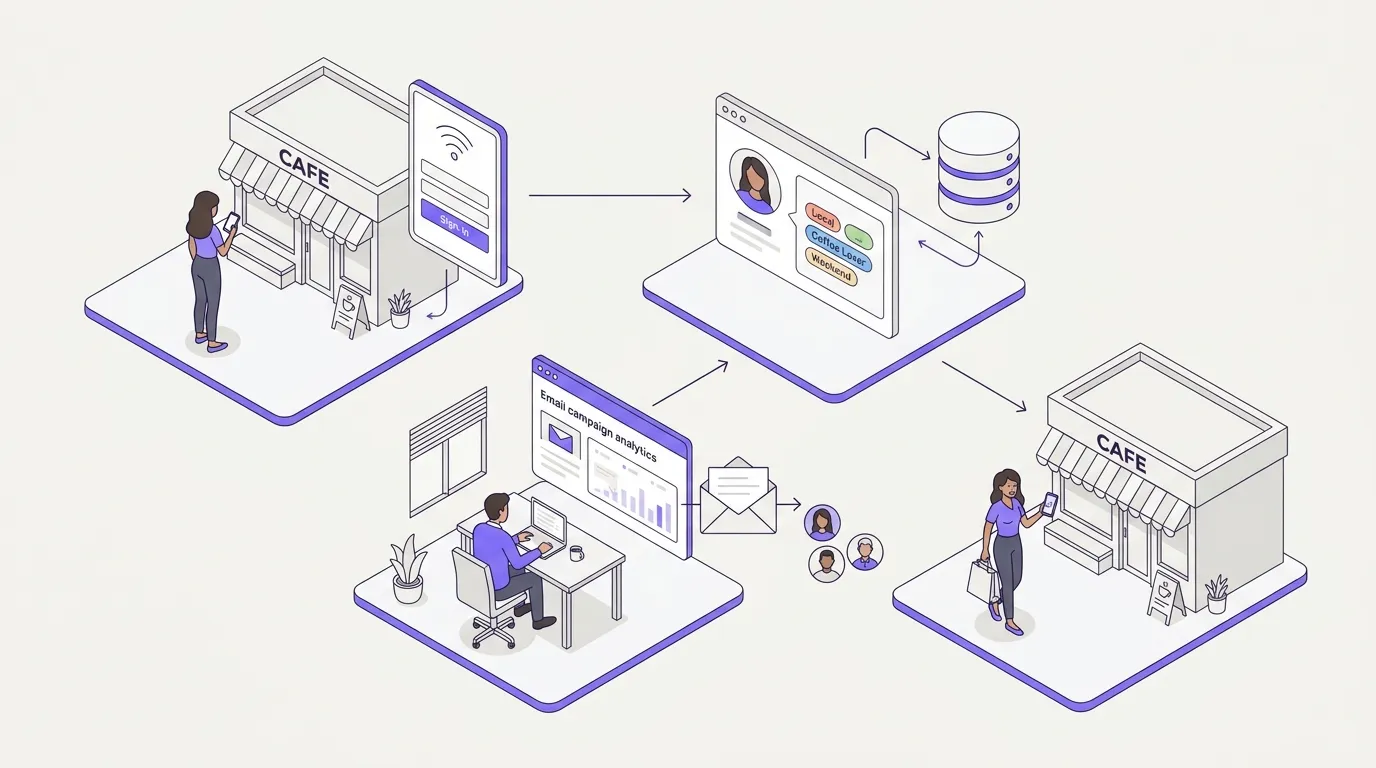 Compliance
CCPA/CPRA-compliant email marketing for venues: a practical checklist
This practical checklist guides venue marketers through the essentials of CCPA/CPRA-compliant email marketing.
Questions
Questions about email compliance
Does using Purple Engage make my email marketing compliant?
No tool is compliant on its own: it depends on how you collect consent and what you send. Purple Engage gives you the mechanisms: double opt-in forms that keep the wording each guest saw, consent recorded per channel with its source, a check before every email, a suppression list that survives re-import, US texts held to 8 a.m. to 8 p.m. in the guest's own time (a pilot the Purple team sets up with you) and erasure through more than 30 registered routines.
Does accepting the WiFi terms count as consent to marketing?
No. Agreeing to the terms lets a guest use the WiFi. Marketing consent is a separate, clear choice, such as a box the guest checks themselves, and only that counts in Purple Engage.
Do I need double opt-in?
US law does not require it, but it proves the address belongs to the person who gave it, which a single box cannot. Purple Engage sign-up forms are always double opt-in, and WiFi sign-ins carry the opt-in the guest gave at the login page.
How long can I keep guest marketing data?
As long as your own policy says, and no longer than you need it. If you have guests in the UK, UK GDPR asks you to justify the period you choose. In Purple Engage you set it in months, and any visit, click or form submission restarts the clock.
What happens when a guest asks to be erased?
Their details are erased everywhere you hold them, and only what the law allows is kept, such as the suppression that stops them being emailed again. In Purple Engage, campaign statistics stay as counts, so your reports still add up.
Who is responsible for compliance, Purple or the venue?
The venue, as the business sending the email, decides the basis for marketing and what is sent. Purple Engage records the basis for each consent and the source it came from, and gives no legal advice.
Guide topics
The other four guide topics
List building and data capture
WiFi email capture
How to turn guest WiFi logins into a consented email list, and what to ask guests for.Campaigns and automation
Venue email campaigns
Which automations and one-off campaigns bring guests back, and when to send each one.Segmentation and targeting
Customer segmentation
How to group guests by what they do, so each group gets the message that brings it back.Analytics and ROI
Email marketing ROI
How to measure the visits and revenue your emails cause, not just the opens they get.
By type of venue
- HotelsStays from Mews and apaleo, and automations that start at checkout.
- RestaurantsWin back regulars, fill quiet weekdays and survey diners after each visit.
How Purple Engage compares
Start with consent you can prove
The free plan is listed at 500 credits a month, with unlimited* contacts and no card needed.